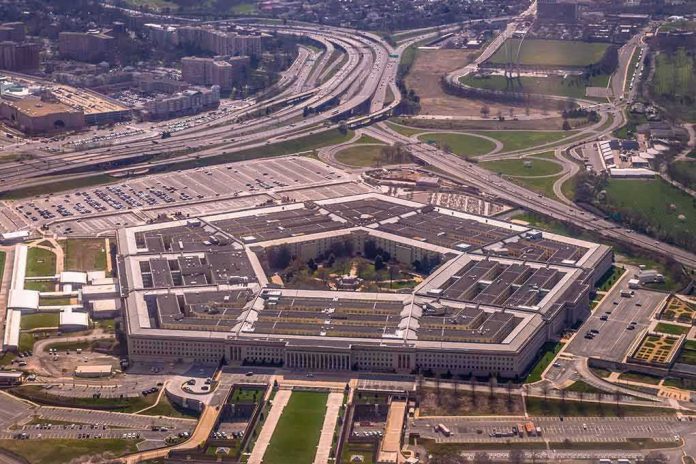
The Pentagon’s problem is not a single failed audit; it is a system of weak internal controls that leaves the world’s largest defense organization unable to prove basic accountability for trillions in assets and exposes its programs to avoidable fraud risk.
The Short Version
- DOD has never earned a clean, department-wide audit opinion; repeated disclaimers stem from evidence gaps and pervasive control weaknesses.
- GAO says longstanding internal-control failures heighten fraud exposure and weaken financial integrity across trillion-dollar operations.
- Audit “progress” coexists with thousands of findings and dozens of material weaknesses; FY2024 alone logged 28 such weaknesses.
- Weapon-system property records—including for F‑35 parts—remain unreliable, compromising both reporting and asset accountability.
- DOD’s revised strategy aims for a clean opinion by end‑2028, but GAO flags unresolved questions: transparency, IT, fraud-risk analytics, and sustainability.
What “failed the audit” actually means—and why it matters
“Failed audit” is shorthand for a disclaimer of opinion: auditors cannot obtain sufficient, appropriate evidence to conclude whether financial statements are fairly presented. In the Defense Department’s case, the disclaimers are not one-off paperwork lapses; they are a pattern across years that GAO ties to entrenched internal-control deficiencies spanning systems, processes, and data quality. A disclaimer does not prove theft. It does demonstrate that the Department cannot reliably prove where all its money and property are, at scale, on demand. In a department managing roughly half of federal discretionary spending, that inability is a governance risk in its own right, independent of any single scandal.
GAO’s language is unambiguous: long-standing control weaknesses both weaken financial management and increase opportunities for fraud against the Department’s vast resources. The risk is structural. When ledgers and asset systems cannot be reconciled, bad actors have more room to move; honest managers, too, are hampered, because they cannot execute or oversee effectively without trustworthy data.
The audit record: progress within components, persistent failure in consolidation
Congress has required full-scope, department-wide audits since fiscal year 2018. Each year through FY2024, the consolidated audit resulted in a disclaimer rather than a clean opinion. Within that overall failure, some components have made headway; several have achieved clean opinions, demonstrating that auditability is possible in pieces of the enterprise. Yet the aggregation of 25 reporting entities into one set of financial statements remains unauditable. For FY2024, the DOD auditor reported 28 material weaknesses—deficiencies so significant they could lead to a material misstatement of the financial statements. Thousands of discrete audit findings accumulate behind those headline weaknesses, documenting issues from IT access controls to reconciliations and property records.
Defense leaders highlight improvement metrics: more standalone entities with passing opinions, and clean opinions that reportedly cover major shares of liabilities and assets. Those are welcome steps. But consolidation is the test the law requires and the one the Department continues to fail. Partial coverage by clean opinions does not cure the evidence gaps that produce a department-wide disclaimer.
Mechanics of failure: property, systems, and the evidence chain
Two mechanisms repeatedly collapse under scrutiny. First, property accountability, particularly for government-furnished and contractor-held materiel tied to major weapon systems. GAO found that DOD had not established procedures sufficient to ensure it could account for and report on F‑35 parts; physical inventory steps did not adequately verify existence or completeness. When the ledger cannot be tied to the warehouse (or the depot shelf, or the flight line), auditors cannot confirm assets, and commanders cannot be fully confident in readiness claims that depend on those parts being where records say they are.
Second, financial systems and data integration. The Department operates a thicket of legacy and modern systems that do not consistently talk to each other, leaving manual reconciliations, unsupported journal entries, and timing gaps that make audit evidence retrieval slow or impossible. GAO links these IT and process issues directly to the disclaimers, and to heightened fraud exposure, because poor segregation of duties, weak access controls, and unverifiable transactions are classic avenues for exploitation.
Fraud-risk management: exposure is documented; loss totals are not
GAO identifies the Department’s fraud-risk management as an unresolved, department-wide oversight problem. It recommends revising DOD’s strategy to institutionalize data analytics for preventing, detecting, and responding to fraud—core capabilities that mature finance organizations consider table stakes. The critical nuance: while exposure is established, the available record does not provide a department-wide dollar estimate of confirmed fraud attributable to the audit failures. Not every discrepancy is theft; some are unsupported costs, timing errors, or plain sloppiness. The audit disclaimers mean “can’t prove,” not “proven stolen.” Conflating those categories—whether to minimize or sensationalize—obscures what policy needs to fix.
The 2028 plan: what is changing—and what GAO says still isn’t
Facing a statutory deadline, DOD has revised its approach with the stated goal of achieving a clean opinion by the end of 2028. The plan emphasizes centralized coordination, heavier technology investment, and streamlined financial reporting. Leaders point to platforms for consolidating data, joint task forces to synchronize audit remediation, and the use of automation and AI to reconcile transactions and assemble audit evidence faster. These moves target the evidence chain that has stymied prior audits.
GAO, however, flags unresolved questions: transparency of progress metrics, accountability for remediation owners, persistent IT control weaknesses, the still-immature fraud-risk analytics program, shortages of trained personnel, and—crucially—whether improvements will be sustained beyond the first clean opinion. It also cautions that a clean opinion is a point-in-time judgment; it does not by itself prove that underlying business processes and internal controls are robust in steady state. GAO has not assessed whether the new approach will succeed; therefore, declaring it inadequate or guaranteed is premature. But neither do dashboards and data lakes substitute for durable control design, consistent execution, and independent validation.
What genuine improvement would look like
Three conditions would indicate reform is taking root. First, end-to-end property accountability that ties the asset record to physical inventory across government and contractor custody, with cycle counts and discrepancy-resolution workflows that pass substantive testing—starting with high-risk portfolios like F‑35 parts. Second, IT general controls that hold under audit: user access, change management, and data integrity across core financial and feeder systems, measured by reduced material weaknesses and faster, complete evidence retrieval. Third, institutionalized fraud-risk analytics—scenario libraries, model governance, false-positive and recovery metrics—embedded across payment, contract, and property processes, not just in pilot form. Progress here should be traceable in fewer repeat findings, smaller backlogs of remediation actions, and component-to-consolidated roll-ups that reconcile without heroic effort.
JUST IN: For the 9th year in a row, the Pentagon failed its financial audit.
44% of its $4.9 trillion in assets didn’t pass their audits.
That’s $2.2 TRILLION.
How many audits does the Government have to fail before Congress investigates for fraud?
— Andrew Lokenauth (@FluentInFinance) November 17, 2026
How to read the next “milestone” announcement
If the Department secures more component clean opinions or even a department-wide clean opinion ahead of or by 2028, treat it as a milestone, not an end state. Ask four questions: Which material weaknesses were fully remediated versus re-scoped? What proportion of the balance sheet relied on workarounds, waivers, or narrow testing windows? How were property and IT control defects addressed in design and in operation, not just papered over by reconciliations? And where are the fraud-risk analytics running in production, with what recoveries and deterrence effects? GAO’s record makes clear that only consistent answers to those questions will convert audit theater into lasting accountability.